
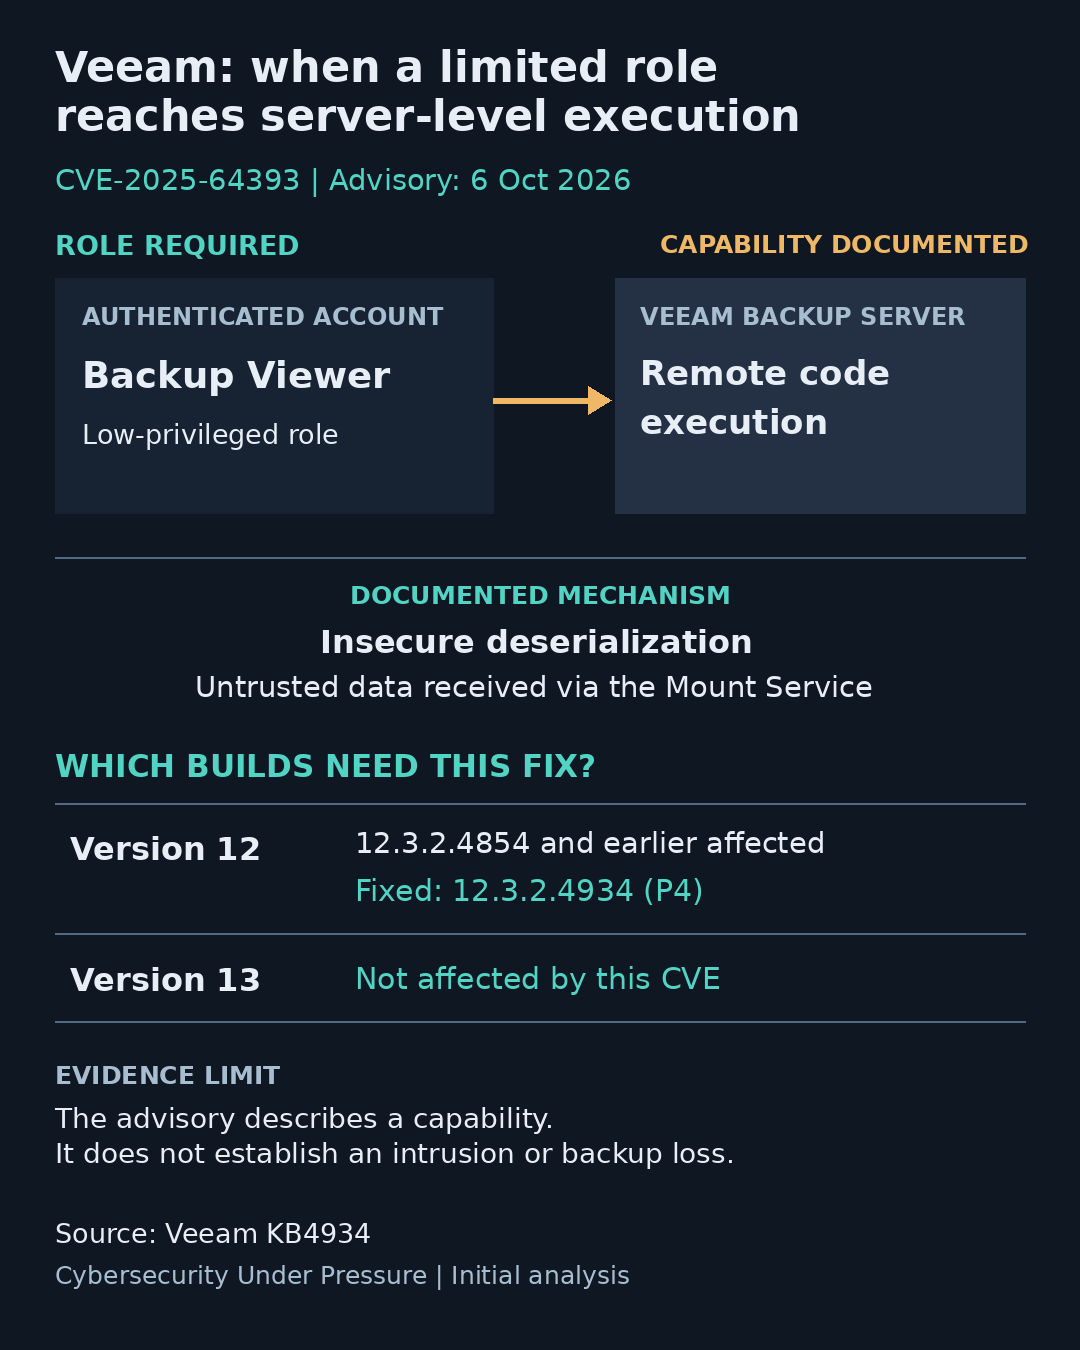
Veeam disclosed CVE-2025-64393 on 6 October 2026. Its advisory describes remote code execution on the Veeam Backup Server by a low-privileged user with the Backup Viewer role. The affected asset is the server used to manage backup and recovery, which makes the authority behind an apparently limited role relevant to recovery planning.
The documented mechanism is insecure deserialization of untrusted data received via the Mount Service. Possession of the Backup Viewer role is a prerequisite. The advisory does not document a complete intrusion sequence, exploitation in the wild, data loss or compromised backups. Those outcomes should not be inferred from the code-execution capability alone.
The affected scope is Veeam Backup & Replication version 12, build 12.3.2.4854 and earlier. The fixed build is 12.3.2 P4, 12.3.2.4934. Veeam explicitly states that version 13 is not affected by this vulnerability. Its CVSS 4.0 rating is 9.4; that rating does not establish the exposure or compromise of a particular deployment.
The professional consequence is a risk to the system used to manage recovery. This is CUP's interpretation of the documented capability, not evidence of a recovery outage. For an affected deployment, use the vendor-supported update path to P4 and check the running build after the change.
The installation path matters. KB4696 permits the patch file only from builds 12.3.2.3617, 12.3.2.4165, 12.3.2.4465 or 12.3.2.4854. Older version 12 installations require the full upgrade ISO. Enterprise Manager, where deployed, must be updated first.
The backup owner should plan the change and any restart, preserve configuration recovery options and validate the backup and restore functions the organisation needs. The identity owner should review accounts holding the Backup Viewer role. Record the deployed build, relevant role assignments and functional validation together. These are CUP's operational recommendations; access restrictions are supplementary precautions, not a vendor-validated fix for this vulnerability.
Recheck this initial analysis if Veeam changes the affected scope, remediation guidance or exploitation evidence. A confirmed intrusion would require separate evidence about the affected deployment and consequences.
Primary sources
- Veeam KB4934, published and updated 6 October 2026. CVE-2025-64393 mechanism, required role, affected scope, fixed build and CVSS rating.
- Veeam KB4696, release and installation guidance inspected 8 October 2026. P4 build, patch eligibility and Enterprise Manager update order.
- CERT-FR CERTFR-2026-AVI-1278, published 7 October 2026. Corroborating advisory for the affected Veeam products.
Continue this decision.
Move from this analysis into a curated route across related incidents, evidence and operating constraints.